AWS with Terraform Tutorial: AWS Basics (2)
How to start building AWS infrastructure with Terraform #
AWS is the world’s leading cloud platform, it is used by a wide range of organizations, from startups to large enterprises, to power their online businesses. AWS offers a wide range of services, including computing, storage, database, networking, analytics, machine learning, and artificial intelligence.
Welcome to our tutorial series where we dive into cloud infrastructure deployment using Terraform or OpenTofu on AWS. In this series, the fundamentals are shown, guiding you through the process of minimizing resource usage and simplifying the deployment complexities associated with cloud infrastructure.
This comprehensive OpenTofu and Terraform tutorial guides you step-by-step through creating infrastructure in AWS using Terraform.
Infrastructure as Code (IaC) helps maintain consistency, enables version control, enhances collaboration among teams, allows for easier replication of environments, streamlines the deployment and management of infrastructure boosting efficiency, and reducing errors in managing complex systems.
Prerequisites #
Read the previous sections of the tutorial, listed in the series index at the end of this page.
AWS Introduction #
AWS is a cloud provider that offers more than 200 services. Many services are equivalent to traditional infrastructure services or products run in an on-premises data center but with added features unavailable at most traditional data centers. All services are available through APIs or the AWS Web Console.
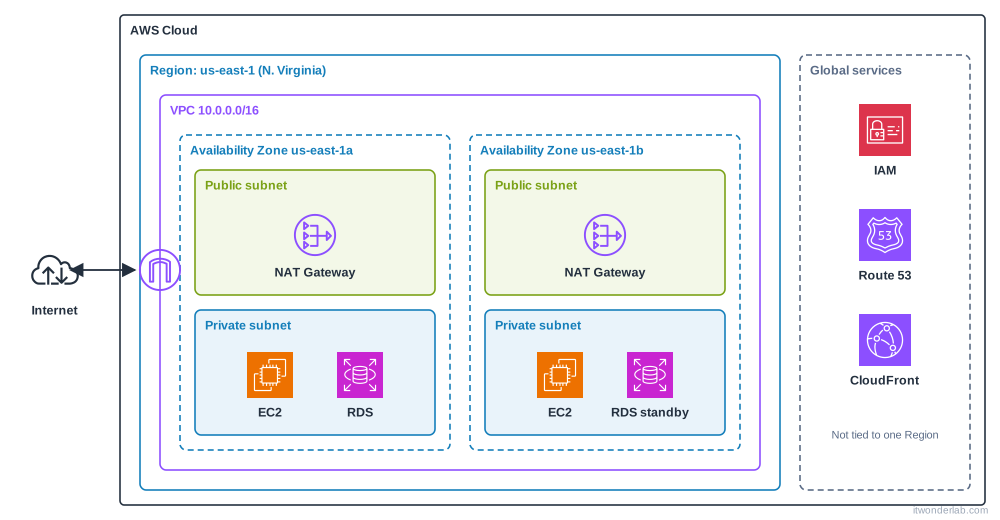
Terraform has an official AWS Provider that lets Terraform configurations define AWS services and manage the AWS infrastructure using code, as IaC.
AWS Free Tier #
The AWS Free Tier is a program that allows users to explore and try out a variety of AWS services for free, up to certain limits. It’s a great way to get started with the cloud without worrying about incurring any charges.
Types of free tier offerings:
- Always Free: These services are available to all AWS customers indefinitely, with limited usage quotas. Some examples include Amazon DynamoDB, Amazon SQS, and Amazon SNS.
- 12 Months Free: These services are free for the first 12 months after signing up for an AWS account, with usage limits, for example small EC2 instances and S3 storage.
- Short-Term Free Trials: These trials usually last for 30 or 60 days and offer full access to specific services to test them out before committing. Examples include Amazon Redshift, Amazon Lightsail, and Amazon Cognito.
Access to the free tier:
- Create an AWS account to access the Free Tier.
- Each service has its own set of usage limits, check limits before using it.
- Unused free tier usage does not roll over to the next month.
- Once free tier limits are exceeded or the free trial expires, usage will be charged.
AWS Services: Compute #
Amazon EC2 #
EC2 stands for Elastic Compute Cloud. EC2 Instances are the equivalent of on-premises servers and are one of the most important services in a Cloud Infrastructure for enterprise applications.
Instances are defined by their CPU/s, Memory, Storage, Networking, and optionally specialized chips.
For the tutorial, we will mostly use Amazon EC2 T4g Instances (Arm-based AWS Graviton2 processors) running Linux. T4g instances are low-cost and burstable (the ability to burst above the baseline level of CPU).
- See more details about Amazon EC2 or Elastic Compute Cloud Service and AWS Auto Scaling.
Amazon ECS #
AWS ECS (Amazon Elastic Container Service) is a fully managed container orchestration service for deploying, managing, and scaling containerized applications using Docker containers. ECS allows users to easily run containerized applications on a cluster of EC2 instances or with AWS Fargate, handling tasks like scheduling, scaling, and load balancing.
- See more details about Amazon Elastic Container Service.
- See the Tutorial on How to use Terraform to create an AWS ECS Fargate Cluster and publish Docker Container Images.
AWS Lambda #
AWS Lambda is a serverless, event-driven computing service designed for running code without the need to provision or manage servers.
In a Lambda environment, servers operate only when triggered by an event to execute code, thereby avoiding idle server charges. This approach significantly reduces costs for short-lived tasks that do not require continuous operation.
Lambda automatically manages servers, scaling them based on the perceived load, such as spikes in traffic or the number of events.
Events like S3 bucket uploads, SNS notifications, DynamoDB updates, background tasks, or API Gateway requests trigger code execution.
Lambda is ideal for microservices and short-lived tasks, but monitoring its cost is crucial as it might reach a point where the expenses surpass running EC2 instances.
AWS Fargate #
AWS Fargate is a serverless computing engine to run containers without having to manage the underlying infrastructure (Kubernetes or Docker). Fargate handles the provisioning and scaling of the infrastructure required to run containers, abstracting away the complexities of server management.
- See the Tutorial on How to use Terraform to create an AWS ECS Fargate Cluster and publish Docker Container Images.
AWS Services: Storage #
Amazon S3 #
Amazon S3, which stands for Amazon Simple Storage Service, is a cloud object storage for any type of data. It’s designed to store and retrieve data from anywhere on the web, offering scalability, security, and high availability. S3 stores data in containers called “buckets.”
S3 is commonly used to store the Terraform State file as a Remote Backend.
- See more details about Amazon Simple Storage Service.
Amazon EBS #
Amazon EBS stands for Amazon Elastic Block Store, the block storage for the persistent data of EC2 instances. Instance block storage for the operating system uses EBS volumes, and it is possible to add multiple volumes and even share volumes across instances using EBS Multi-Attach.
- See more details about Amazon Elastic Block Store. For a shared file system, see Amazon EFS.
Amazon FSx #
Amazon FSx is a fully managed file storage service. It provides scalable and high-performance file storage for Windows applications in the cloud.
FSx supports the Server Message Block (SMB) protocol, making it compatible with Windows file servers and integrated with Active Directory. It also offers features like data deduplication, data compression, and backup options for efficient file storage and management.
FSx can also be used to share a filesystem between multiple servers when cloud-native options like S3 are not feasible.
Amazon S3 Glacier #
The S3 Glacier storage classes are low-cost cloud storage tiers of AWS S3. It is designed for long-term data archiving and backup, where data retrieval speed is less critical. Glacier offers a very cost-effective solution for storing large amounts of data that may not be accessed frequently.
- See more details in Amazon Simple Storage Service.
AWS Services: Database #
Managed relational databases like MySQL, PostgreSQL, etc.
Amazon RDS and Amazon Aurora #
AWS RDS stands for Amazon Relational Database Service. It’s a fully managed service provided by Amazon Web Services (AWS) that simplifies the setup, operation, and scaling of relational databases in the cloud.
See more details about Amazon Relational Database Service and Amazon Aurora, a MySQL and PostgreSQL-compatible engine built for the cloud.
Amazon DynamoDB #
Amazon DynamoDB is a fully managed highly scalable, and serverless NoSQL database. DynamoDB is designed for high performance, low latency, and seamless scalability.
Amazon DynamoDB is commonly used as a locking mechanism for the Terraform state stored in S3. See AWS DynamoDB.
Amazon Redshift #
Amazon Redshift is a fully managed, petabyte-scale data warehouse service provided by Amazon Web Services (AWS). It’s designed for large-scale analytics and data warehousing, enabling businesses to analyze vast amounts of data efficiently and cost-effectively.
AWS Services: Artificial Intelligence and Machine Learning #
A suite of tools for developers and data scientists to build, train, and deploy machine learning models.
Amazon Bedrock #
Amazon Bedrock gives you access to a variety of foundation artificial intelligence (AI) models (large language models (LLMs) and other AI models pre-trained on massive amounts of data) from different providers.
Amazon SageMaker #
Amazon SageMaker is a fully managed machine learning (ML) service provided by Amazon Web Services (AWS). It enables developers and data scientists to build, train, and deploy machine learning models at scale. SageMaker simplifies the end-to-end process of machine learning, making it accessible to a wide range of users with different skill levels.
Amazon Rekognition #
Amazon Rekognition enables developers to add image and video analysis capabilities to their applications without the need for deep expertise in machine learning. Rekognition uses advanced deep-learning algorithms to analyze and extract meaningful information from visual content.
Amazon Polly #
Amazon Polly enables developers to integrate text-to-speech (TTS) capabilities into their applications. Polly converts input text into lifelike speech using advanced deep-learning technologies. It supports multiple languages, voices, and customization options, making it a versatile solution for generating natural-sounding speech.
Amazon Lex #
Amazon Lex enables developers to build conversational interfaces, or chatbots, into their applications. It uses natural language understanding (NLU) and automatic speech recognition (ASR) to process and interpret user input, allowing applications to respond with appropriate actions or information
AWS Services: Security, Identity, & Compliance #
A suite of tools and AWS services to help build secure, compliant, and well-governed cloud environments. This category encompasses services that focus on identity and access management, data protection, compliance management, threat detection, and overall security of AWS resources.
AWS Identity and Access Management (IAM) #
See AWS IAM. AWS Identity and Access Management (IAM) is a web service provided by Amazon Web Services (AWS) that enables users to securely control access to AWS services and resources. IAM allows administrators to manage users, groups, roles, and permissions within their AWS accounts, ensuring secure and fine-grained control over who can perform specific actions and access particular resources.
AWS Key Management Service (KMS) #
See AWS KMS. AWS KMS is a managed service that enables users to create and control the encryption keys used to encrypt their data. It integrates with other AWS services to ensure secure data storage and transmission.
AWS Secrets Manager #
See AWS Secrets Manager. AWS Secrets Manager helps in securely storing and managing sensitive information, such as API keys, passwords, and database credentials. It facilitates the rotation and retrieval of secrets in a secure manner.
Amazon Cognito #
Amazon Cognito provides identity and access management for web and mobile applications. It supports user authentication, registration, and account recovery, making it easier to manage user identities.
AWS Certificate Manager (ACM) #
See AWS ACM. ACM simplifies the process of managing SSL/TLS certificates for applications deployed on AWS. It provides automated certificate issuance and renewal.
AWS WAF #
See AWS WAF. AWS WAF is a web application firewall that helps protect web applications from common web exploits. It allows users to define customizable rules for filtering malicious traffic.
AWS Shield #
AWS Shield is a managed Distributed Denial of Service (DDoS) protection service. Its primary purpose is to safeguard AWS applications and websites against the impact of DDoS attacks by detecting and mitigating malicious traffic in real-time.
AWS Security Hub #
AWS Security Hub provides a comprehensive view of the security state of an AWS environment. It aggregates and prioritizes security findings from various AWS services and third-party tools.
Amazon GuardDuty #
Amazon GuardDuty is a threat detection service that continuously monitors malicious activity and unauthorized behavior in AWS accounts. It uses machine learning and threat intelligence for effective threat detection.
AWS Services: Networking & Content Delivery #
Tools and services to build robust and scalable network architectures, ensuring efficient data delivery and connectivity. Amazon VPC enables users to create isolated virtual networks, while Amazon Route 53 offers scalable and reliable domain name system (DNS) services. AWS Direct Connect facilitates dedicated network connections to AWS, enhancing data transfer reliability. Amazon CloudFront, a content delivery network (CDN), accelerates content delivery globally, improving user experience by minimizing latency.
Amazon VPC #
An AWS VPC (Virtual Private Cloud) is a virtual network dedicated to an AWS account. It enables users to launch AWS resources, like EC2 instances, within a logically isolated section of the AWS Cloud. With a VPC, users have control over their network environment, including IP address ranges, subnets, route tables, and network gateways. VPCs allow for greater security, customization, and connectivity options, enabling users to create a network that mirrors a traditional data center setup in the cloud.
- See more details about Amazon Virtual Private Cloud.
Amazon Route 53 #
Amazon Route 53 is a scalable and highly available Domain Name System (DNS). It is designed to route end-user requests to globally distributed endpoints, such as web applications or resources, and effectively connects user requests to the corresponding AWS resources.
- See more details about Amazon Route 53 (DNS Service).
Amazon CloudFront #
Amazon CloudFront is a content delivery network (CDN) service provided by AWS. It is designed to deliver content, including web pages, videos, images, and other static or dynamic assets, to users with low latency and high data transfer speeds. CloudFront accelerates content delivery by caching it at edge locations distributed globally.
- See more details about Amazon CloudFront Content Delivery Network.
AWS Direct Connect #
AWS Direct Connect enables dedicated and private network connections between an organization’s on-premises data centers or corporate networks and the AWS cloud. This service bypasses the public internet allowing a reliable, low-latency, and consistent connection.
AWS Site-to-Site VPN #
Provides a Virtual Private Network (VPN) service that allows organizations to establish secure and encrypted connections between their on-premises networks or remote offices and their Amazon Virtual Private Cloud using IPsec (IKEv1/IKEv2) with static routes or Border Gateway Protocol (BGP) for automatic route propagation.
AWS Services: Management, Monitoring & Governance #
Set of tools and services to help users efficiently manage their AWS resources, monitor performance, and implement governance policies. These services are essential for optimizing resource utilization, ensuring security and compliance, and gaining insights into the operational health of AWS environments.
AWS CloudWatch #
See AWS CloudWatch. AWS CloudWatch is a monitoring service that collects and tracks metrics, logs, and events from AWS resources. It provides a unified view of operational health and performance, facilitating proactive management.
AWS CloudTrail #
See AWS CloudTrail. AWS CloudTrail records API calls made on AWS resources, providing a history of activity for security, compliance, and operational analysis. It helps users understand who did what and when within their AWS accounts.
AWS Config #
AWS Config continuously monitors and records configuration changes to AWS resources, allowing users to assess the impact of changes, troubleshoot configuration issues, and maintain compliance.
AWS Systems Manager #
See AWS Systems Manager. AWS Systems Manager provides a unified user interface for managing AWS resources. It includes capabilities for automation, patch management, parameter store, and session manager for secure instance access.
AWS OpsWorks #
AWS OpsWorks was a configuration management service that supported Chef and Puppet. It reached its end of life in 2024. Alternatives are AWS Systems Manager and Ansible.
AWS Service Catalog #
AWS Service Catalog enables organizations to create and manage catalogs of IT services, making it easy to provision and deploy approved resources. It helps enforce governance and compliance.
AWS Organizations #
See AWS Organizations. AWS Organizations allows users to consolidate multiple AWS accounts into an organization that they create and centrally manage. It simplifies billing, applies policies across accounts, and facilitates resource sharing.
AWS Budgets #
AWS Budgets helps users set custom cost and usage budgets, allowing them to monitor and control their spending on AWS resources. It provides alerts when actual costs exceed defined thresholds.
AWS Management Console #
The AWS Management Console is a web-based interface for interacting with AWS services. It provides a unified and intuitive platform for managing and configuring resources.
AWS Well-Architected Tool #
The AWS Well-Architected Tool helps users review their workloads against AWS best practices. It provides recommendations for improving security, reliability, performance efficiency, cost optimization, and operational excellence.
AWS Config Rules #
AWS Config Rules enable users to define rules that automatically evaluate configurations against desired settings. It helps in ensuring compliance with organizational policies.
AWS Auto Scaling #
See AWS Auto Scaling and the tutorial AWS Auto Scaling. AWS Auto Scaling automatically adjusts the number of instances in an Auto Scaling group to maintain application availability and performance. It helps optimize resource utilization based on demand.
AWS Services: Other #
Amazon has over 200 cloud services, for a basic AWS Terraform tutorial only a handful of services are used although adding new services is relatively easy once Terraform basics have been covered.
- Amazon SQS – Simple Queue Service for asynchronous messaging.
- Amazon SNS – Simple Notification Service for publish/subscribe messaging and notifications.
- Amazon EKS – managed Kubernetes.
- Amazon ElastiCache – managed in-memory cache.
- Amazon Kinesis – Real-time data streaming service.
- AWS IoT Core – Connect and manage IoT devices.
Common AWS Questions #
Is AWS more expensive than on-premises? #
There is no easy answer as it depends. AWS services include much more functionality than traditional on-premises services and the pricing model is pay-per-use, on-premises infrastructure is usually acquired (not rented) and has additional costs like networking, security, electricity, cooling, engineers, and many more fixed costs.
Some companies are moving away from the Cloud, like 37signals. Still, those companies have economies of scale, extremely high requirements and predictability, and most importantly can attract the exceptional talent needed to properly run the local infrastructure.
Most companies, even multinationals, have limited access to top talent, knowledge, or the predictability needed to excel on-premises. Cloud seems to be more expensive than on-premises, but you get much more than what you get on-premises and the cloud expenditure can be constantly optimized with proper guidance and commitment agreements.
Is AWS better than GCP or Azure? #
The “best” choice depends on your specific needs and priorities, our experience, as an SME (small company) offering SaaS on top of AWS to some of the biggest companies in the world, but maybe for different startups, needs, or clients other cloud providers are more appropriate. SMEs can benefit from AWS recognition in the Enterprise world by leveraging their cloud provider availability or options, regions, tools, and services, along with its security capabilities and certifications.
Next Steps #
Continue with Terraform AWS Provider, or see the full series index.